Install on XCP-ng / Xen Orchestra
Before you start
You need:
- the DC Netscope XVA, downloaded from easyvirt.com,
- a Xen Orchestra account DC Netscope will read the inventory with. A read-only account is recommended,
- a shell access (SSH or console) to each XCP-ng host whose traffic you want to see,
- an IP address for DC Netscope, or a DHCP network,
- these network openings:
| Flow | From | To | Port |
|---|---|---|---|
| Web interface | Your users | DC Netscope | 443/tcp |
| Inventory | DC Netscope | Xen Orchestra | 443/tcp |
| NetFlow | XCP-ng hosts (Open vSwitch) | DC Netscope | 9000/udp |
Import the XVA
In Xen Orchestra, open Import > VM, pick the pool, drop the XVA file and choose the storage repository. Click
Import, then attach the virtual machine to the network of your choice.
Do not start it yet: its settings come first.
Set the network and the administrator account
DC Netscope reads its settings from cloud-init. Give it a JSON document such as:
{
    "email": "admin@example.com",
    "os_password": "a-strong-password",
    "ip_mode": "static",
    "static_ip": "192.168.1.50",
    "static_netmask": "255.255.255.0",
    "static_gateway": "192.168.1.1",
    "dns_ip": "192.168.1.1",
    "xo": {
        "url": "xo.example.com",
        "username": "dcnetscope-readonly",
        "password": "xo-password"
    }
}emailandos_passwordcreate the first administrator of DC Netscope. The password is also the one of therootaccount of the virtual machine.ip_modeisdhcp,static, orcloud-initto let cloud-init configure the network itself. Thestatic_*fields are ignored indhcpmode.xois optional: with it, DC Netscope connects to Xen Orchestra on its own, and the next step is already done.
See Appliance settings for all the settings.
To confirm
How to hand this document to an imported XVA from the Xen Orchestra interface (DC Netscope reads it from
/tmp/cloud_init_conf). Without cloud-init, write the same settings in YAML in /etc/dcnetscope.yml from the
console of the virtual machine, and reboot it: see the manual configuration.
Start the virtual machine. After a few minutes, its console shows the address of DC Netscope: open
https://<DC Netscope address> in your browser and log in with the account you defined.
Connect Xen Orchestra
Skip this step if you gave the xo settings above: check only that the status is green.
-
Open the administration interface, and go to the
Servicestab.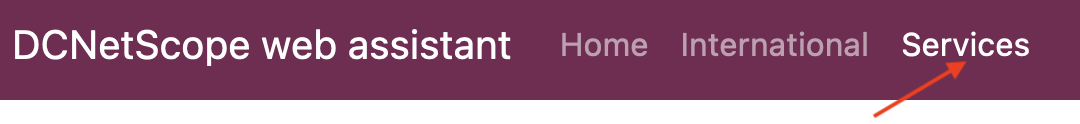
-
In
Connected infrastructures, chooseXen Orchestra, type the address of Xen Orchestra, the user and the password, and clickAdd a new connector. -
Check that the status of Xen Orchestra is green.
Send the flows of Open vSwitch
XCP-ng hosts switch the traffic of the virtual machines with Open vSwitch, which exports it in NetFlow. This is set on each host, from its shell, not from Xen Orchestra.
-
List the bridges of the host, and spot the ones carrying the traffic of your virtual machines (
xenbr0here):ovs-vsctl showThe bridges are listed with their ports: the
vifports are the network interfaces of the virtual machines.210ec8ad-efdd-4f23-8522-2eebdcda28e1 Bridge xenbr0 fail_mode: standalone Port vif4.0 Interface vif4.0 Port xenbr0 Interface xenbr0 type: internal Port eth0 Interface eth0 ovs_version: "2.17.7" -
Send the flows of the bridge to DC Netscope,
192.168.1.50here:ovs-vsctl -- --id=@nf create NetFlow \ targets=\"192.168.1.50:9000\" \ active_timeout=60 \ add_id_to_interface=true \ -- set Bridge xenbr0 netflow=@nftargets: the address of DC Netscope and the port of its NetFlow collector,active_timeout: how often, in seconds, the flows still open are exported,add_id_to_interface: adds the identifier of the interface to the exported flows.
-
Check the export:
ovs-vsctl list netflowThe
targetsline should read["192.168.1.50:9000"].
Repeat for every bridge and every host.
The export does not survive a reboot of the host
Open vSwitch forgets this setting when the host reboots: run the command again from a startup script or from your automation tool.
Note
The firewall of DC Netscope, and the ones between the hosts and DC Netscope, must let 9000/udp through.
Check that the flows arrive
Open the Dashboard. Within a few minutes, the collect summary shows the traffic received from the hosts, and the flows of your virtual machines appear with their names.
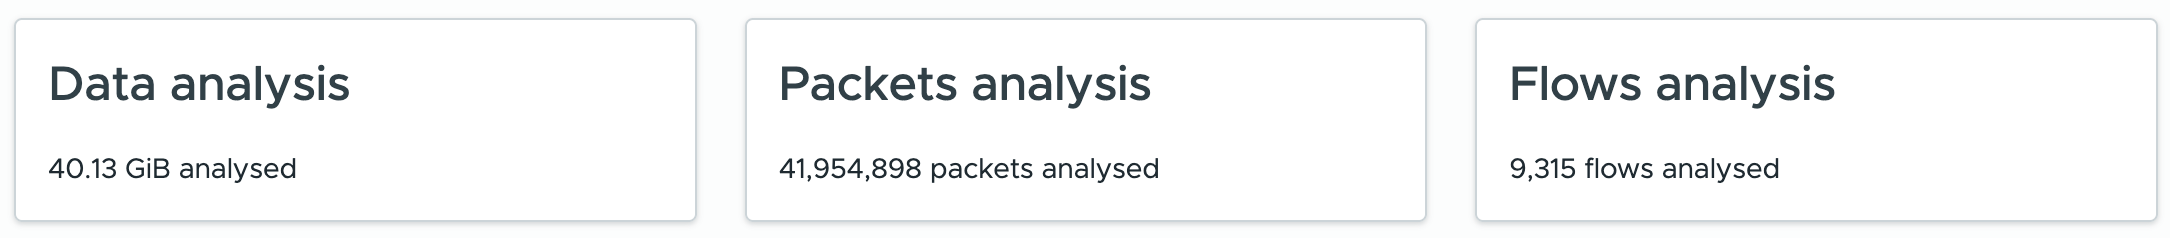
Nothing shows up? Check that 9000/udp is open from the XCP-ng hosts to DC Netscope, run ovs-vsctl list netflow
on the hosts (a rebooted host has lost its export), and have a look at the
troubleshooting page.
Next steps
- Activate your license: a 15 days trial license is active from the installation.
- Manage the users, or connect your Active Directory.
- Group your applications to read the flows between them.